CVE-2024-26152
CVE.org · Published
- Record status
- Published
- Identifier year (not publication year)
- 2024
- Source publication
- Source updated
- Imported by cveboard
- Source snapshot
- cve_2026-10-24_midnight_baseline ·
CNA source text (English)
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 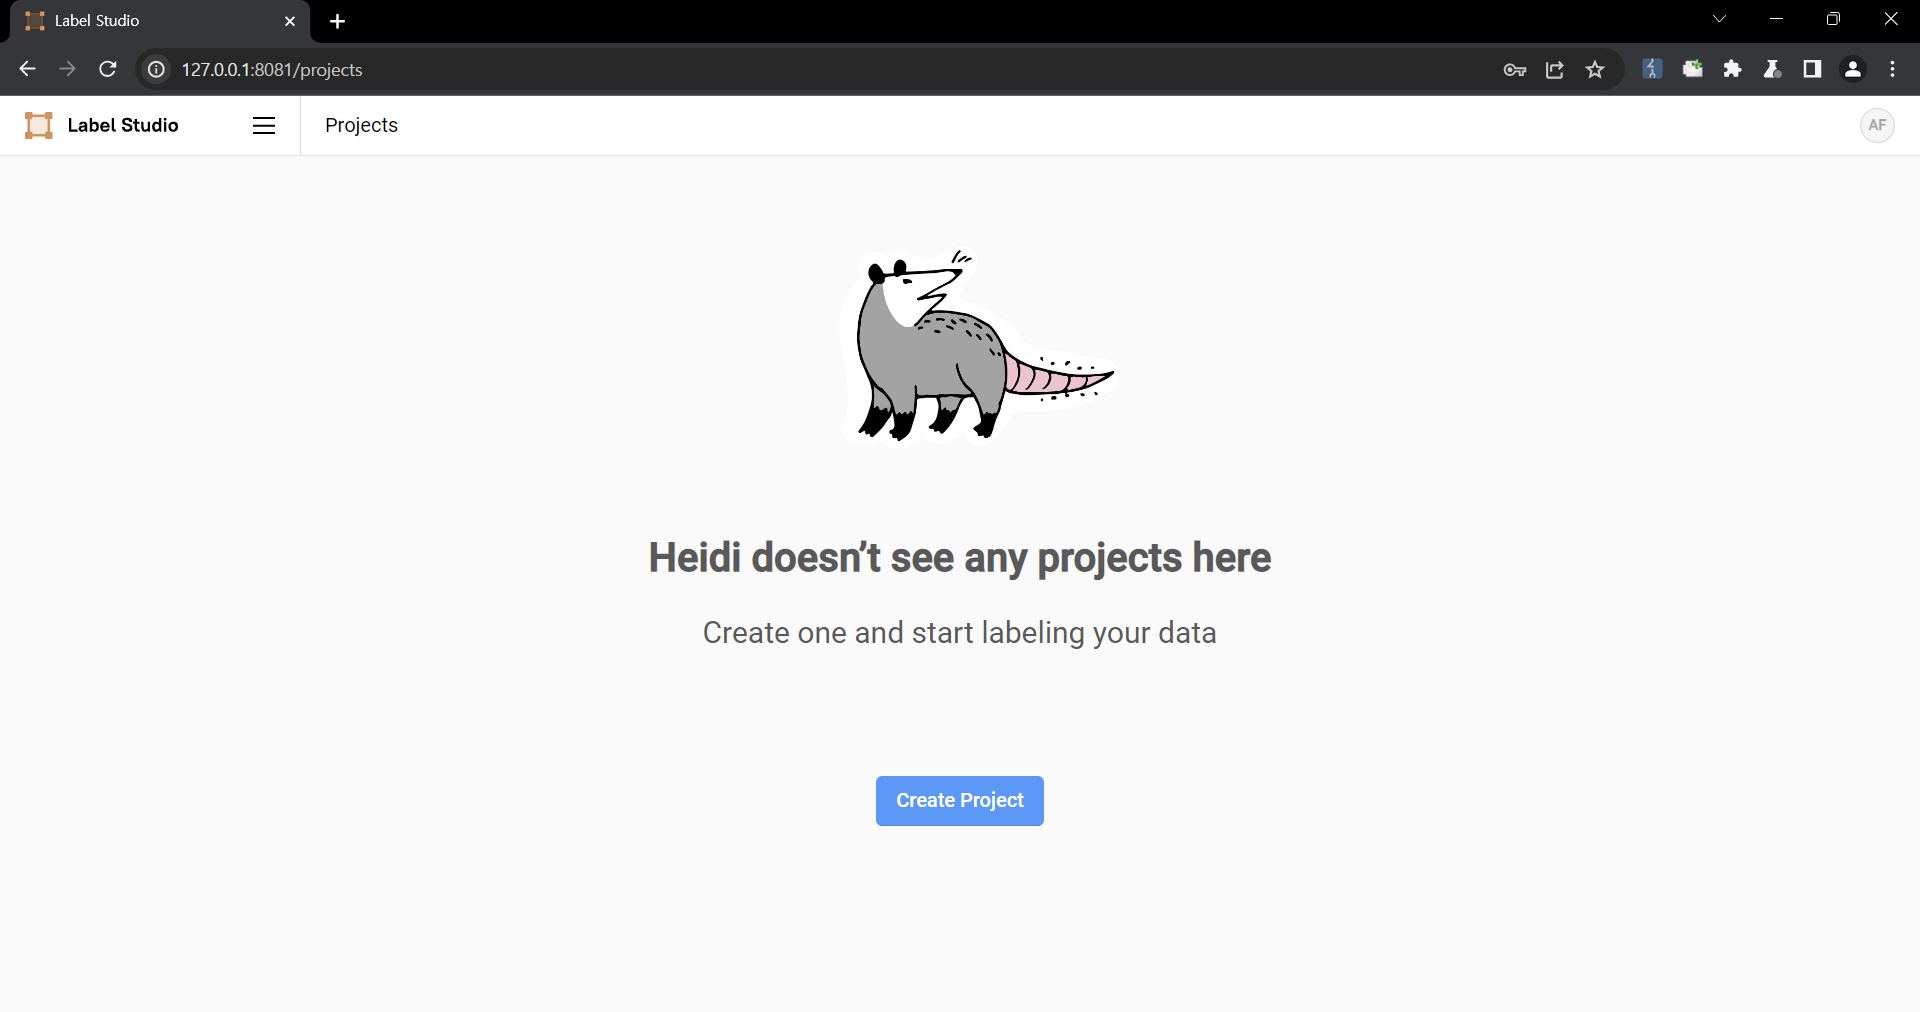 2. Upload a file containing the payload using the "Upload Files" function. 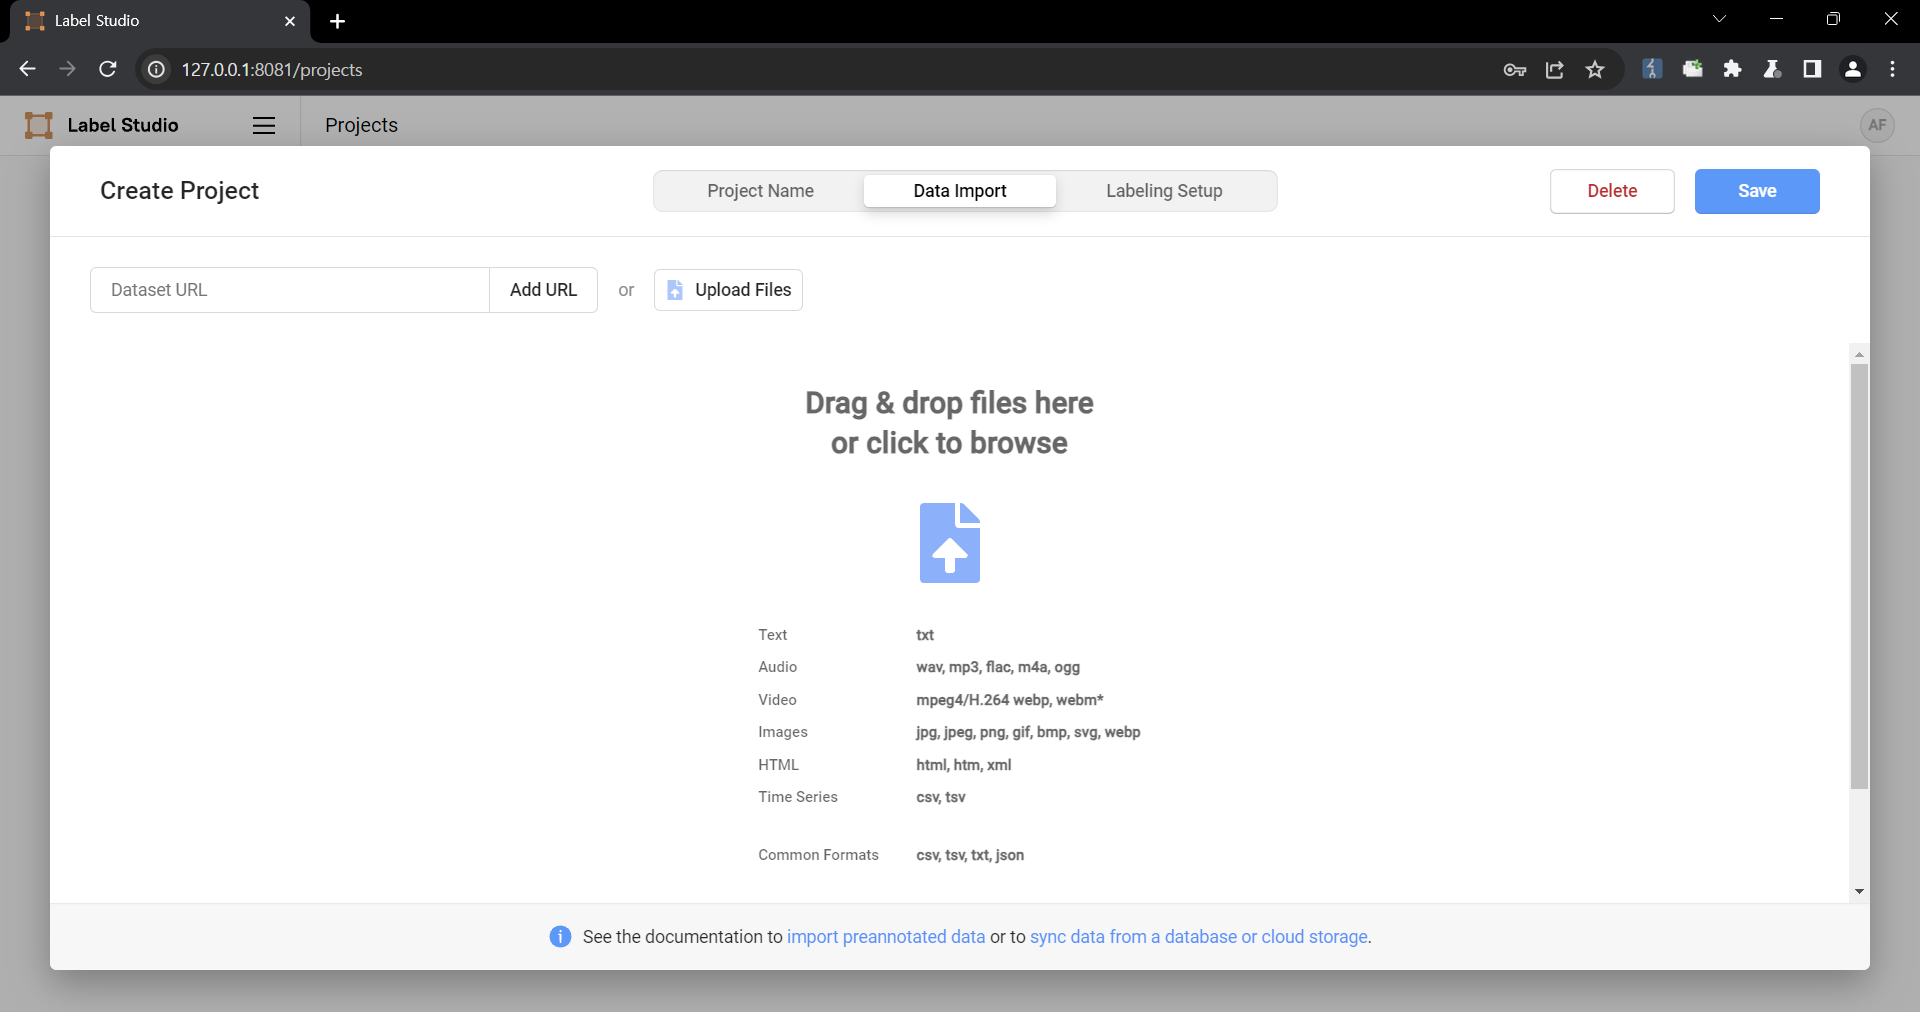 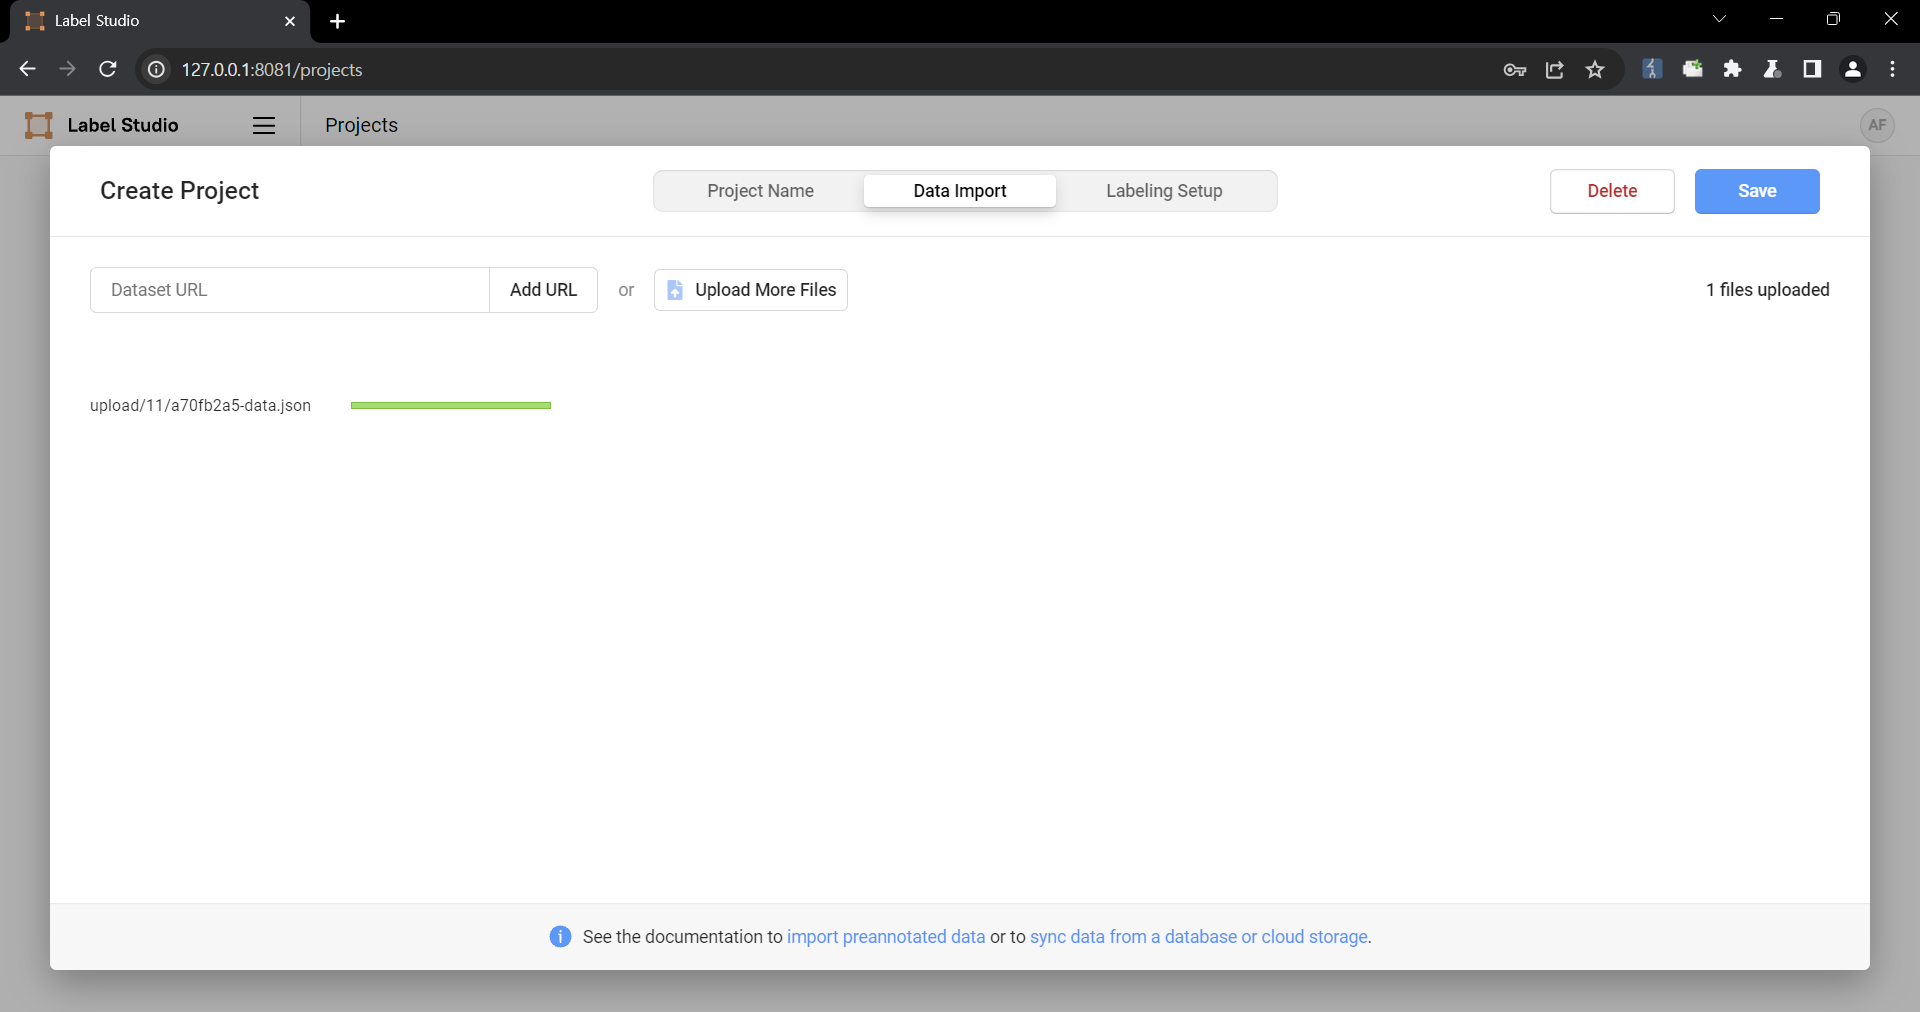 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 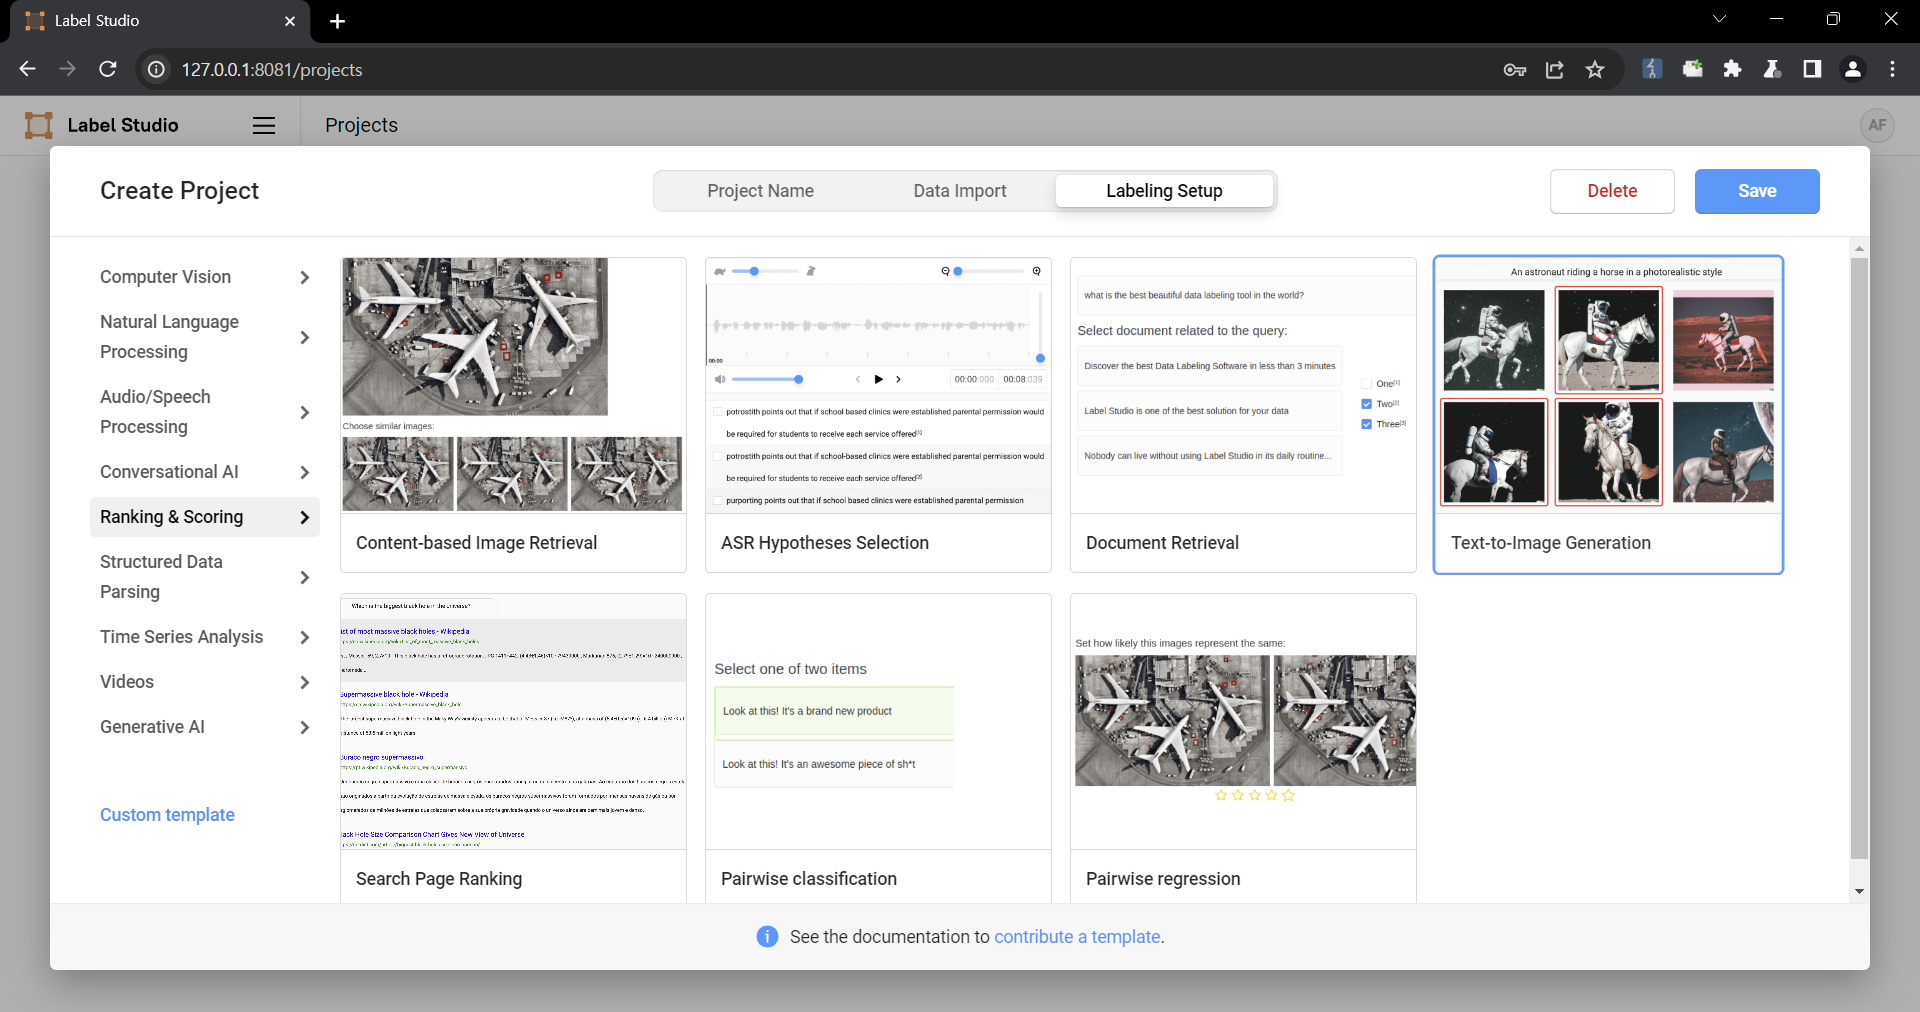 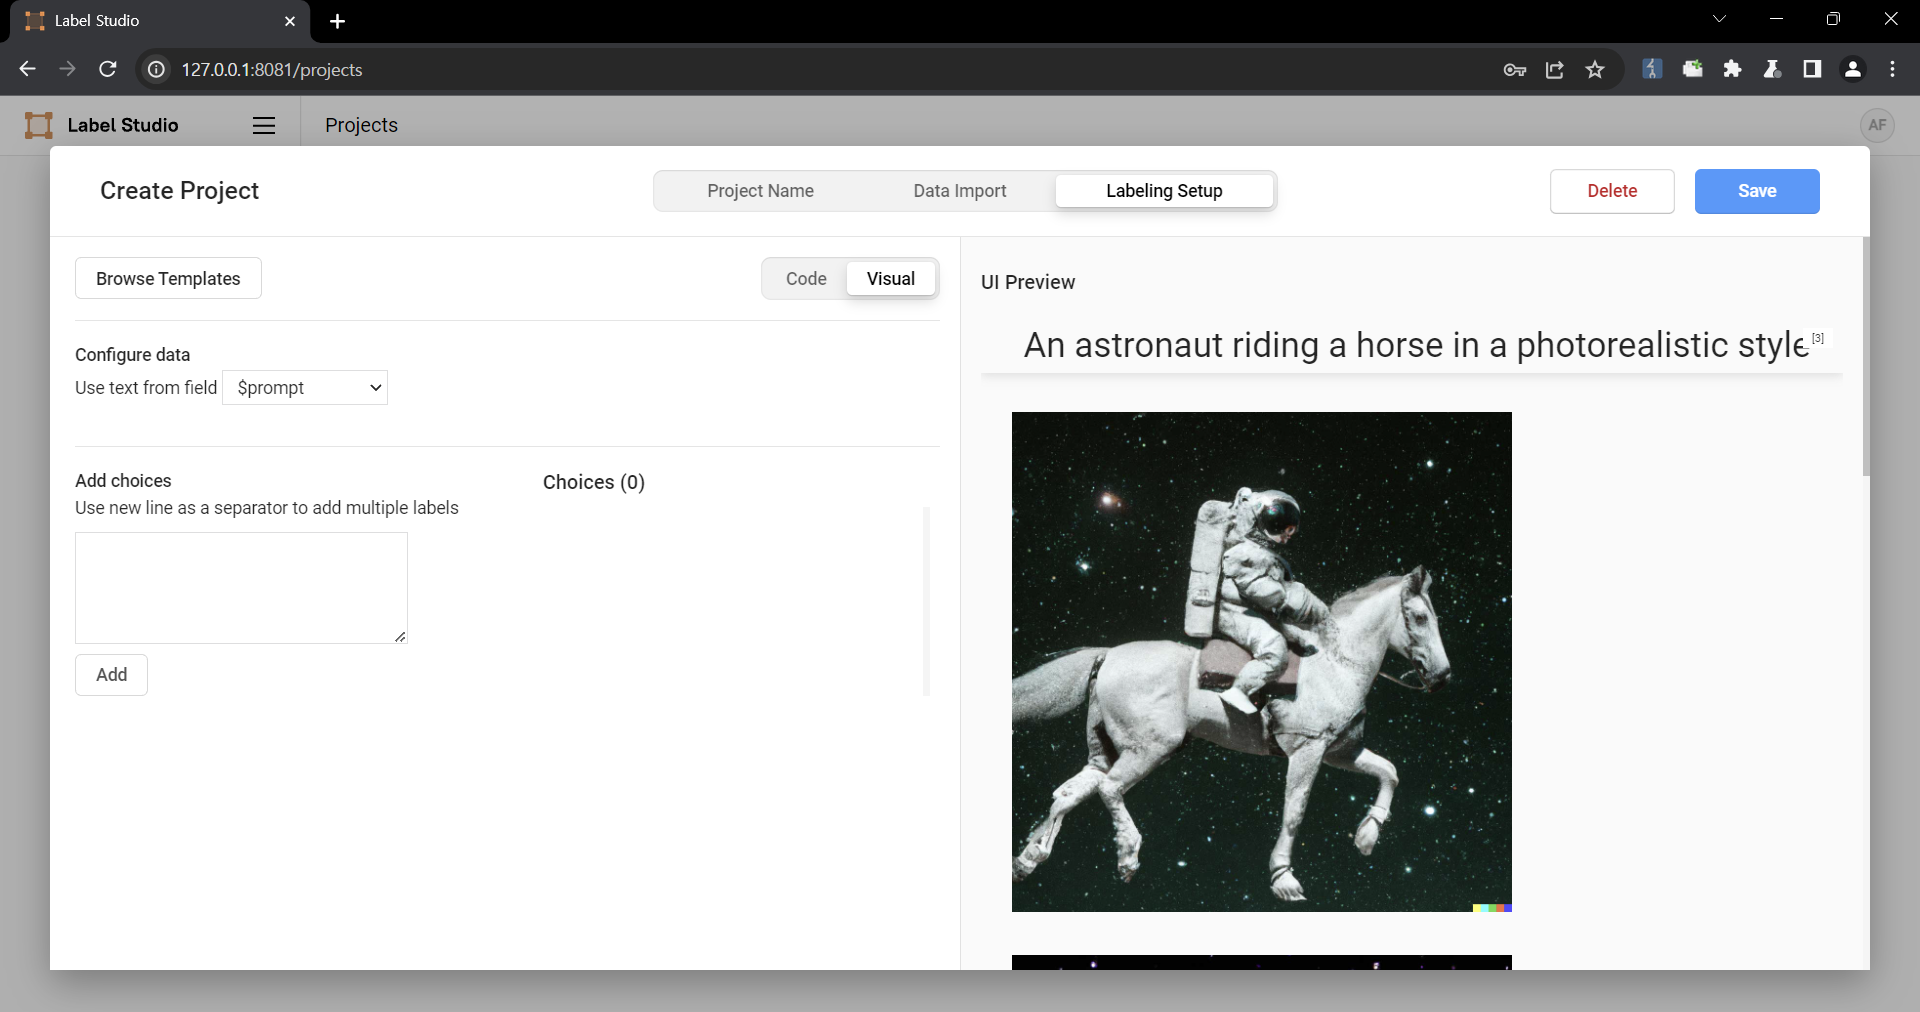 4. Select a task 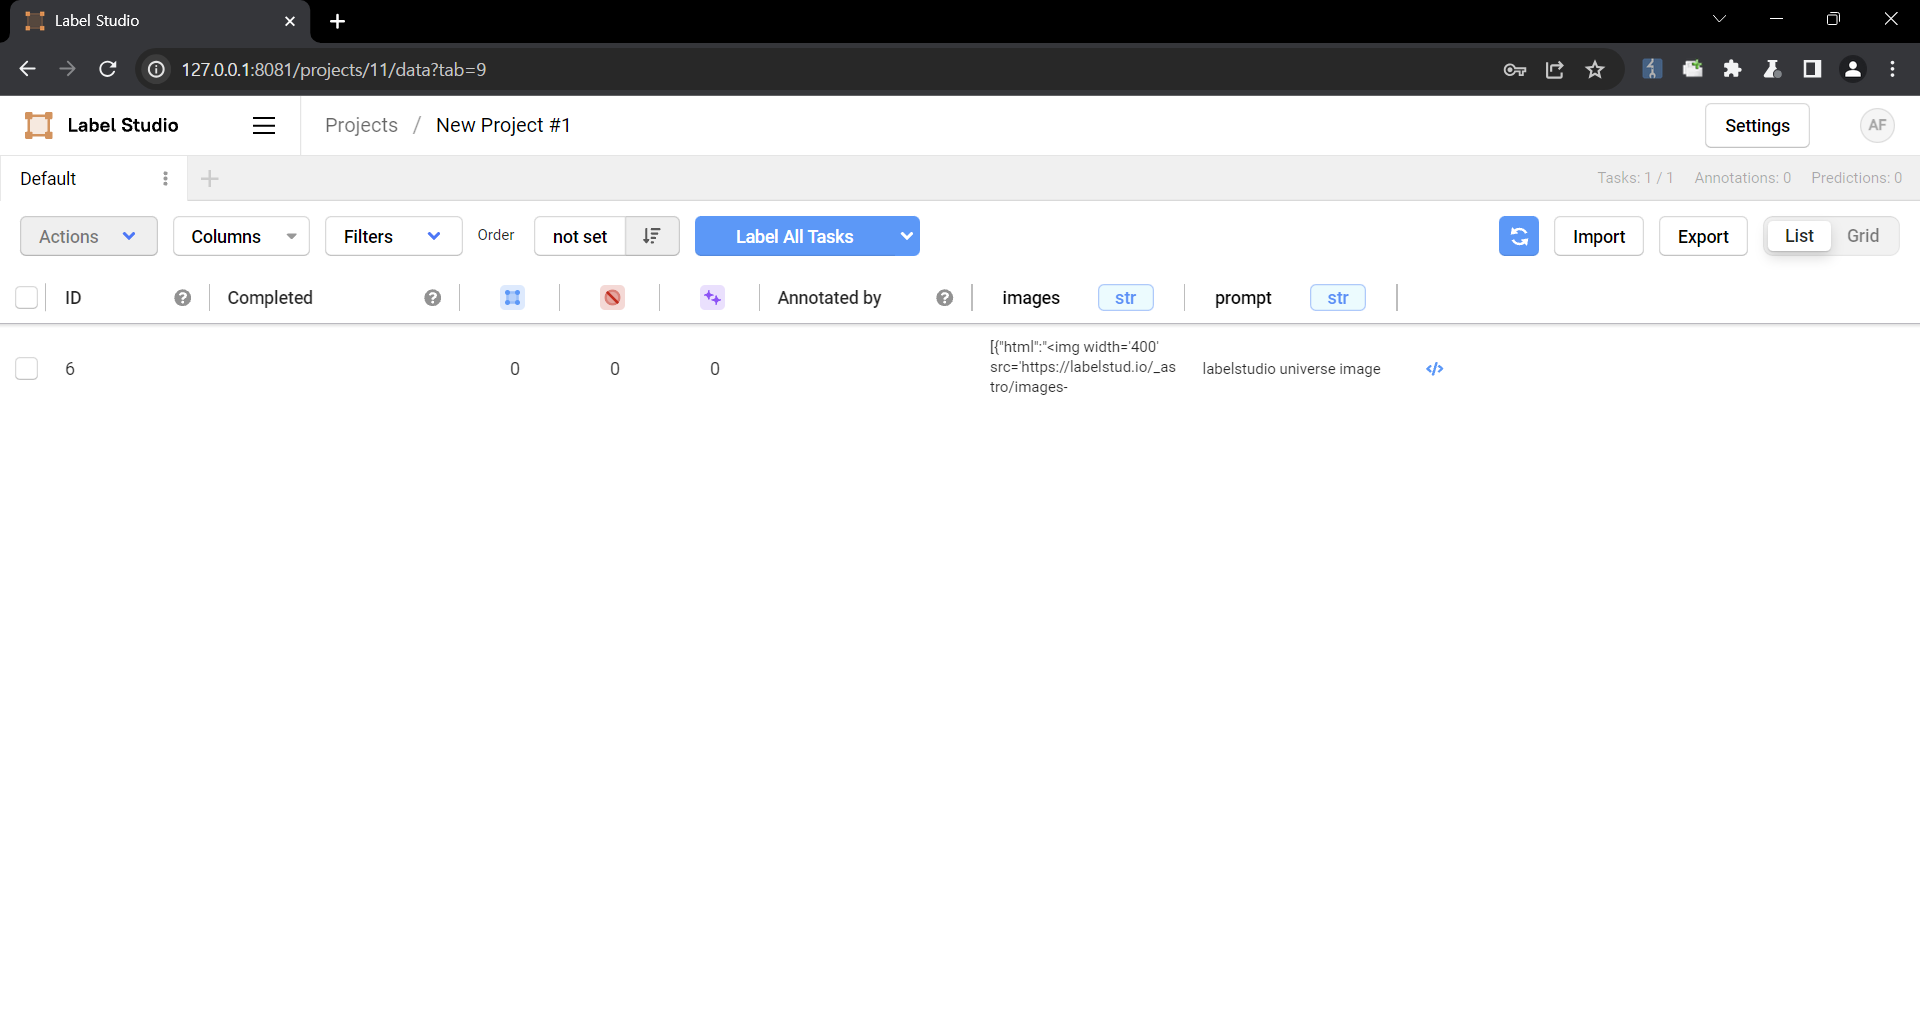 5. Check that the script is running 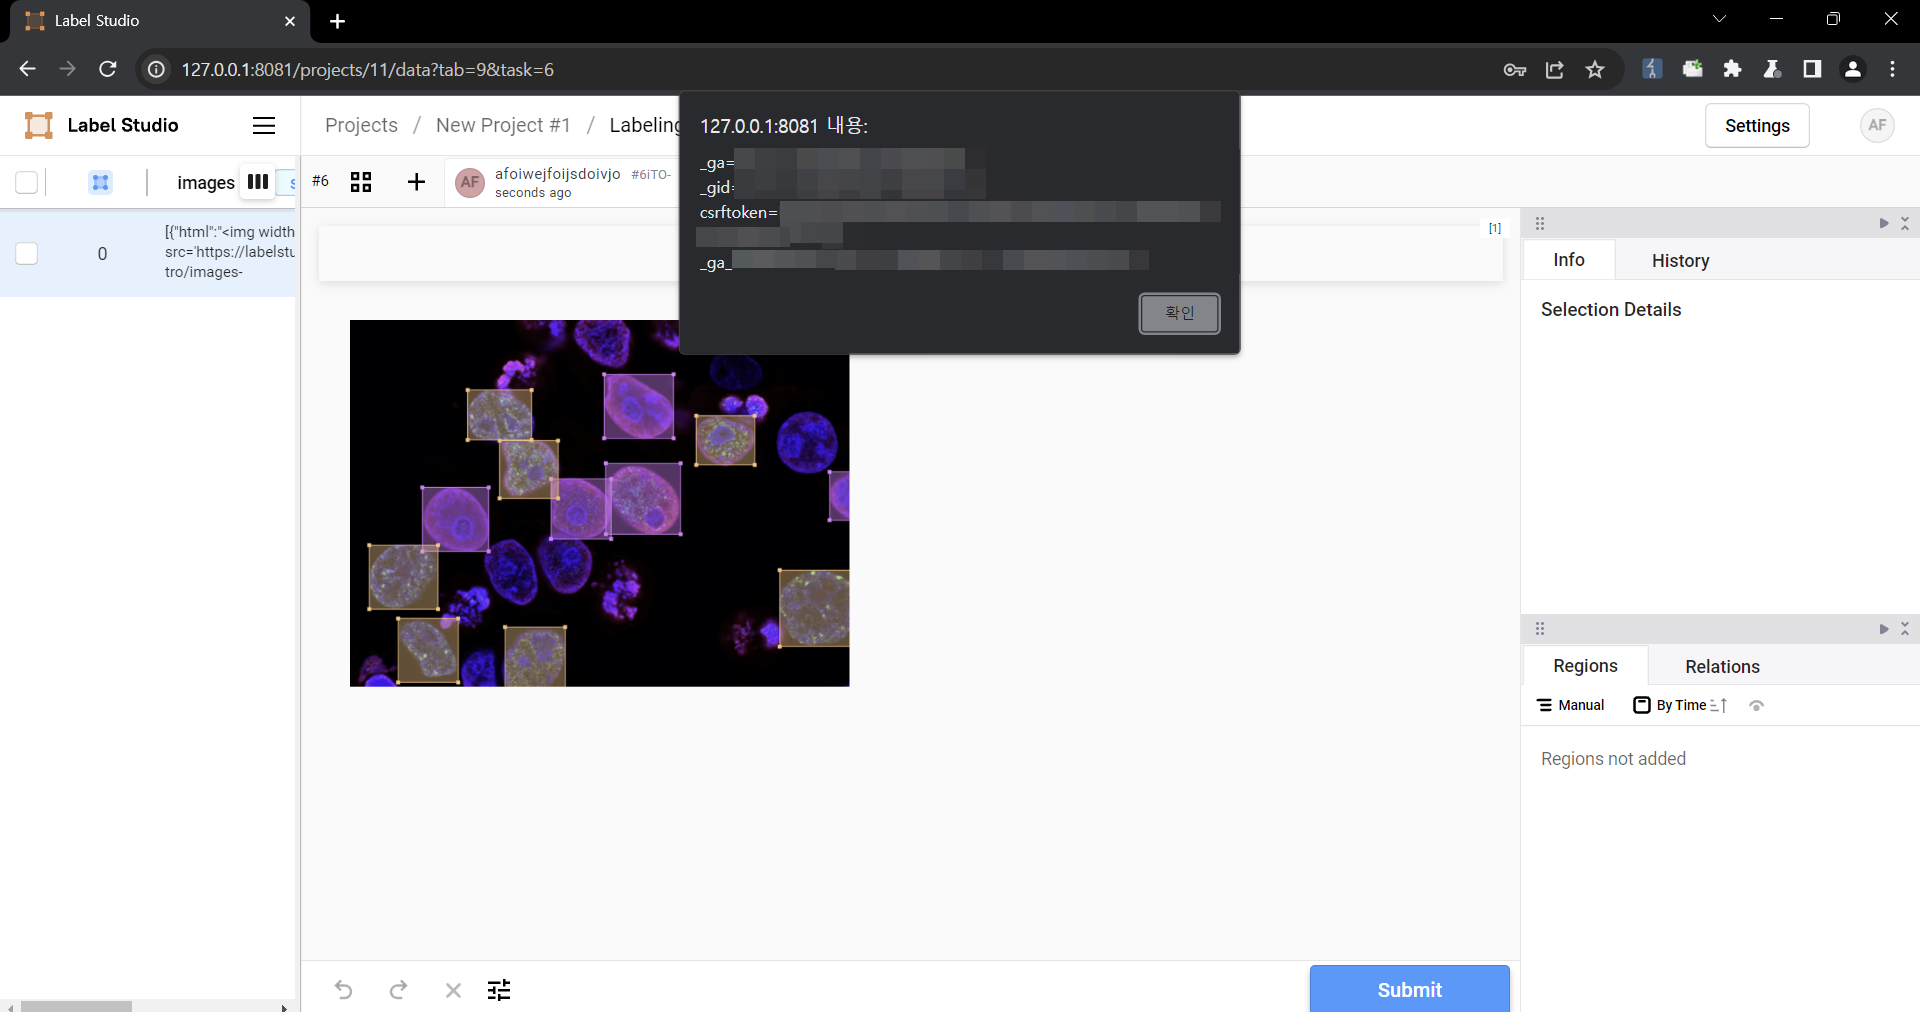 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Scoped product and version facts
Fix information unknown; no fixed version is derived here. Missing information does not prove that no fix exists.
Exploitation unknown; this catalogue does not assess exploitation.
label-studio
- Vendor
- HumanSignal
- Product
- label-studio
- Platforms
- Unknown
- Default status
Unknown
| Version (version) | Status (status) | Version scheme (versionType) | Exclusive end (lessThan) | Inclusive end (lessThanOrEqual) | Status changes (at → status) |
|---|---|---|---|---|---|
| < 1.11.0 | affected | Unavailable | Unavailable | Unavailable | None listed |